

Manage API keys
Generate an API key
An API key allows you to use Hyperline’s API or integrations such as Zapier. As a Hyperline admin:- Go to your workspace Settings, section API
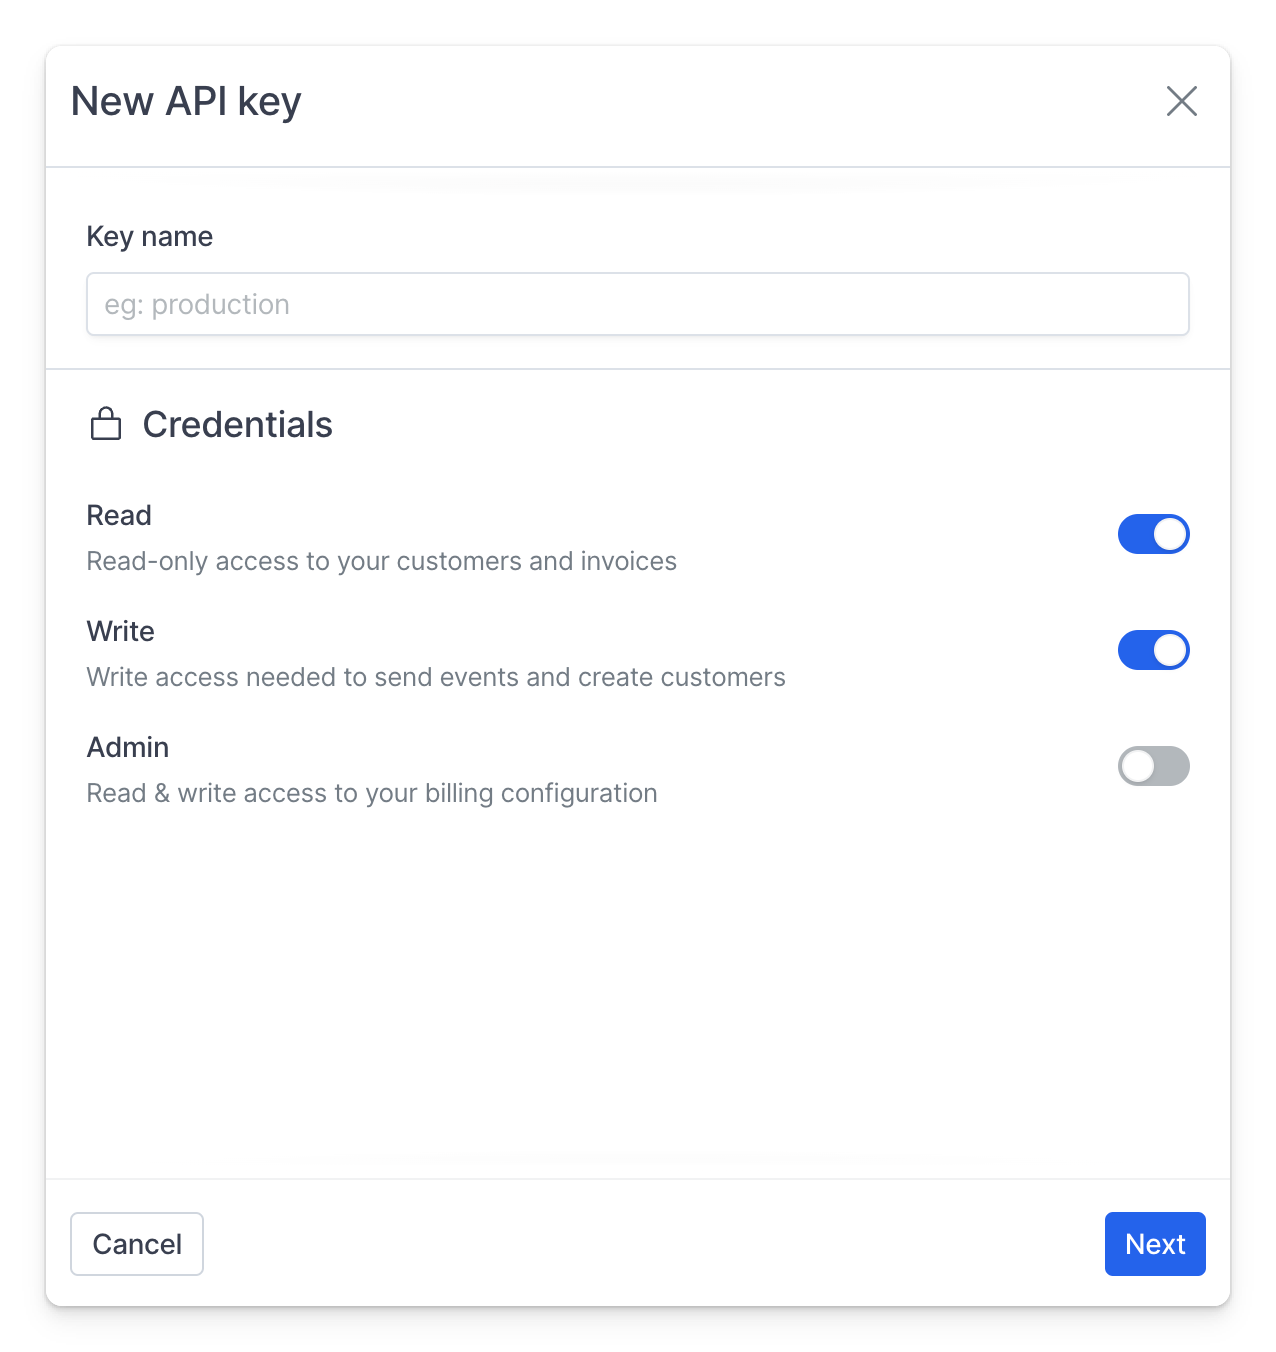
- Click + New API key
- Add a name for this key, and select the appropriate scopes (in most cases you’ll need read/write access)
- Copy the key and store it in a safe space. You won’t be able to see it later in Hyperline
API keys are prefixed either with
prod_ or test_ to easily identify and
distinguish them between environments.Use an authentication token
You must provide an API key or access token with every API call, specified in theAuthorization header after a Bearer prefix. All requests happen using HTTPS.
For example:
We also support HTTP Basic Authentication, where the
username is the API key
and the password is left blank, but we recommend using Bearer Authentication
because it’s simpler for debugging.Keep your data safe
Treat your API keys as highly sensitive information. Think of a token like a password. You should only give tokens to services you fully trust. Anyone who obtains a leaked token could use it maliciously. They can provide someone with access to all of your Hyperline data. If you suspect a token has been compromised, revoke it and replace it with a new one.Revoke a key
Workspace admins can permanently revoke tokens from the API Settings in Hyperline. To revoke a token, click the… icon on the line of the key name, then Delete to permanently delete it. You can’t recover a deleted key.